
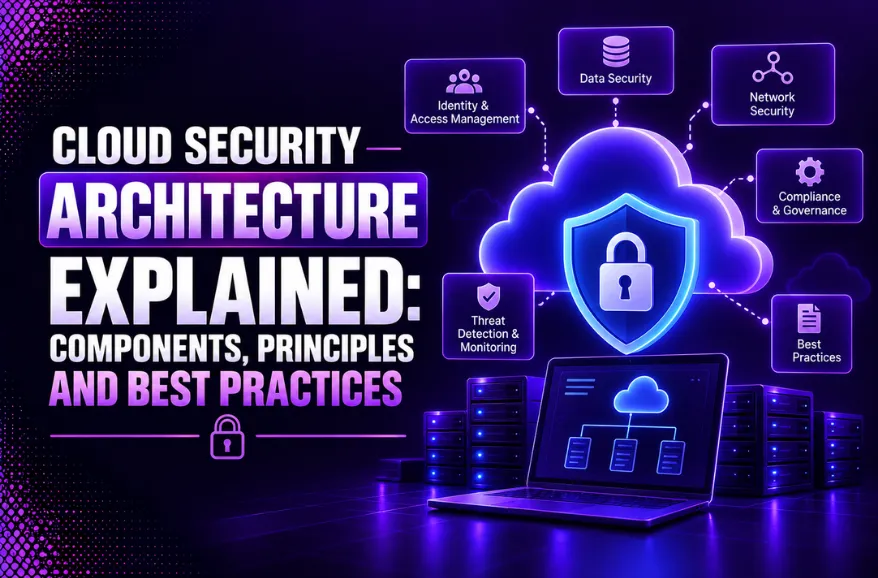
Cloud security architecture implies the systematic plan that prevents cyber threats to cloud-based applications, data, users, and infrastructure. It integrates identity control, network protection, encryption, monitoring, and governance to build a secure cloud environment. A powerful cloud security structure aids organizations to minimize risks, achieve compliance needs, and work securely on the public, private, or even in hybrid clouds. This guide narrates the main building blocks, principles, and models. Lastly, it also includes best practices that enable organizations to establish a resilient cloud security strategy.
Why Cloud Security Architecture Matters in Modern Enterprises
Cloud security architecture is a critical requirement due to the growing investments of enterprises in cloud platforms in order to store information, execute applications, and scale. When trying to embrace the cloud without a proper security structure, an organization can be exposed to data breaches, intrusion, compliance and impairing downtime. A robust architecture secures the privacy of susceptible resources and does not compromise the speed, flexibility, or scalability that make cloud computing worthwhile.
What Is Cloud Security Architecture?
Cloud security architecture refers to a systematic method of security against cyber threats to cloud-based data, applications, networks and infrastructure. It integrates:
- Security mechanisms
- Risk management
- Compliance measures
These ensure that enterprise systems remain confidential, trusted and available.
Understanding Secure Cloud Architecture
Components of a secure Cloud architecture are:
- Identity and access management
- Data encryption
- Network protection
- Application security
- Monitoring and governance
These layers work together to minimize vulnerabilities. It ensures that sensitive resources are located in safe environments. Also, it can be accessed only by those users and systems with authorization.
Why Cloud Security Is Different from Traditional IT Security
Old software-based IT security typically guards against internal breaches via a fixed perimeters in the on-premises network. Security in the cloud is distributed, dynamic and ubiquitous, covering:
- Identities
- APIs
- Workloads and data in public, private and hybrid clouds
How Cloud Security Architecture Works
It does so through various controls like:
- Multi-factor authentication
- Role-based access
- Encryption
- Firewalls
- Constant monitoring
- Planning for incidents.
These measures help identify threats at an early stage, act as a line of defense to restrict access to the system. It ensures that data is kept secure while being used, and enable swift recovery in the event of an incident.
Core Components of Cloud Security Architecture
Identity and Access Management (IAM)
Without IAM users cannot use cloud resources for themeslves. Implementation of role-based access controls, multi-factor authentication, and the principle of least privilege credential policies can help eliminate bad actors.
Network Security and Segmentation
Segmentation separates cloud workloads into safe zones, which restricts subsequent movement in an attack. Micro-segmentation, Virtual private clouds, and firewalls assist in limiting possible breaches.
Data Encryption and Cloud Data Protection
The data should be encrypted in rest, transit and where necessary in processing. Good key management is needed to maintain confidentiality and integrity.
Workload and Application Security
Secure-by-design controls are needed in applications, APIs, containers, and cloud workloads. Frequent configuration, vulnerability and secure coding are used to avoid exploitable vulnerabilities.
Monitoring, Logging and Threat Detection
Real-time monitoring enables the detection of abnormal activity and ensures a quick response to any incident. Centralized logging, monitoring and anomaly detection along with a focus on regulatory compliance all enhance overall visibility of your cloud environment.
Cloud Security Frameworks That Guide Enterprise Security
Shared Responsibility Model
The shared responsibility model helps to outline what the cloud service provider is responsible for protecting (for example, infrastructure). Compared to the customer’s responsibility (for example, configurations, access controls, and data). This division is used to prevent holes that intruders may be trying to exploit.
NIST and CIS Security Frameworks
NIST’s Cybersecurity Framework provides a flexible, enterprise-wide method using functions of: Identify, Protect, Detect, Respond, and Recover. CIS Controls offer practical and prioritized benchmarks for AWS, Azure and GCP.
ISO 27001 and Industry Compliance Standards
ISO 27001 provides guidelines for an information security management system. Whereas ISO/IEC 27017 provides cloud-specific guidance for both cloud providers and cloud customers. Compliance for payment data and regulated workloads is backed up by other standards, such as PCI DSS and FedRAMP.
Principles of Effective Cloud Security Architecture
Least Privilege Access
Limit the granting of rights, only grant users and systems the permissions they need to do their job. IAM, role-based access control and multi-factor authentication are critical to protecting against unauthorised access and containing the impact of compromised credentials.
Defense-in-Depth Strategy
Implement security controls in more than one interdependent layer (e.g., network segmentation, encryption, intrusion detection systems, endpoint control, etc.). These controls reduce the likelihood of a single security failure compromising the whole environment.
Continuous Monitoring and Visibility
Scan activities in the cloud. It assists in:
- Identify misconfiguration
- Questionable activity
- Threats in the early stages
Maintaining visibility helps to make incident response fast and audit preparation ready.
Automation and Security by Design
Architect security in from the ground up and automate enforcement. Better consistency reduces human error. Therefore, one can maintain compliance easily as cloud environments grow.
Zero Trust Cloud Security: Why It’s Becoming the Standard
What Is Zero Trust?
At the core of Zero Trust are these two words: never trust, always verify. Every access request is continuously authenticated, authorized and monitored. Rather than relying on user, device or application security due to its presence within the network. The new security perimeters are identity, rather than network location.
Applying Zero Trust in Cloud Environments
For cloud, hybrid and multi-cloud, Zero Trust offers MFA, IAM & conditional access, device-health checks, encryption, secure APIs, and micro-segmentation. It provides access to user, device, location, risk and resource sensitivity. It continuously monitoring provides for detection of anomalies and restrict lateral move.
Benefits and Implementation Challenges
Zero Trust includes a reduced attack surface, enhanced compliance, better visibility, and secure remote work and cloud adoption. But problems like old systems, complicated identity management, culture, a lack of skills, and the need for ongoing growth arise. Instead of a single implementation, this can prove challenging.
Cloud Security Controls Every Organization Should Implement
Multi-Factor Authentication (MFA)
MFA enhances users to authenticate their identity using various parameters which reduce uselessness of stolen passwords to attackers. It provides an important level of security to cloud accounts and assists to avoid unauthorized access.
Role-Based Access Control (RBAC)
RBAC provides permissions according to the job role of a user, and the least privilege principle is followed. This will restrict access to required resources minimizing insider risk and the effects of breached accounts.
Encryption for Data at Rest and in Transit
Use robust algorithms like AES-256 to encrypt stored data and provide security on data on a transit like TLS. Frequent key changes and giveaway keys given by the customers further enhance security of information.
Security Information and Event Management (SIEM)
SIEM systems combine logs, track user-activity and identify suspicious occurrences in real-time. This visibility assists security teams to identify abnormalities, investigate and take action before threats stimulate.
Cloud Infrastructure Security Best Practices
Secure Network Configuration
Use firewalls, intrusion detection and secure virtual private networks (VPNs) to control traffic and secure your data in transit. Use network segmentation and the least-privilege model to restrict your attack surface.
Protecting Virtual Machines and Containers
Patch those virtual machines and containers. You can encrypt data at rest and in motion. Monitor your workloads for any signs of suspicious activity.
Managing APIs and Cloud Services Securely
The top three of these, strong authentication with MFA, on the provider side and a strong IAM policy with the principle of least privilege on your side, are your allies in defending yourself. Leverage native tools such as:
- AWS Shield
- AWS WAF
- Azure Security Center
Regular Vulnerability Assessments
Perform security audits on a frequent basis. Automated vulnerability scans, along with testings for incident response, should be performed regularly. CSPM, along with SIEM (Security Information and Event Management) tools, detect misconfigurations and raise alerts.
Cloud Security Best Practices for Businesses
Common Cloud Security Challenges and How to Overcome Them
| Cloud Security Challenges | Description | How to Overcome It |
| Misconfigured Cloud Resources | Public storage buckets, weak access permissions, and unencrypted data can expose sensitive information to unauthorized users. | Use Cloud Security Posture Management (CSPM) tools, encrypt sensitive data, and conduct regular configuration audits to identify and resolve security gaps. |
| Insider Threats and Privileged Access Risks | Weak authentication and excessive privileges can increase the risk of unauthorized access or misuse of sensitive resources. | Apply the principle of least privilege, enforce multi-factor authentication (MFA), and implement privileged access management. It also monitors user activity for suspicious behavior. |
| Data Privacy and Regulatory Compliance | Regulations such as GDPR, HIPAA, and CCPA require organizations to maintain appropriate data protection and privacy controls across cloud workloads. | Strengthen compliance checks, encrypt sensitive data, and conduct regular configuration audits to identify gaps and maintain compliance with applicable regulations. |
| Multi-Cloud Security Complexity | Using multiple cloud providers can create inconsistent security controls and limited visibility across different environments. | Standardize security policies, centralize monitoring, and use cloud-native security tools across environments to improve visibility and maintain consistent protection. |
Choosing the Right Cloud Security Solution
Why Businesses Partner with Cloud Security Experts
Conclusion
Cloud engineering design plays a crucial role in security of contemporary businesses. A combination of (IAM, network segmentation, encryption, workload protection, monitoring, and Zero Trust principles) enables organizations to create a reliable, scalable cloud environment. The best cloud security system is proactive, automatic and continuously enhanced. Companies administering effective security measures, awareness systems to their employees and professional assistance can minimize cyber risks and can comfortably speed up the process of deploying the cloud.
Frequently Asked Questions
Q1. What is cloud security architecture?
Cloud security architecture is the policy, control, technology, and trust boundaries strategy. It keeps identities, data, applications, networks, and control planes secure in cloud environments.
Q2. What are the main components of cloud security architecture?
Technology, controls and policies comprise the core of cloud security components of the architecture.
Q3. How does Zero Trust improve cloud security?
Zero Trust enhances cloud security by shifting from a passive, context-less ‘trust first, verify later’ approach to continuous, context-aware verification of all users, devices and workloads.
Q4. Which cloud security framework should businesses follow?
It’s not possible to get a single cloud security framework. Companies should put together their own according to their size, sector rules, and what service providers would demand.
Q5. What are the biggest cloud security risks for enterprises?
The top cloud security threats that enterprises face primarily include human factor, improper configuration and complex identity management.
Leave a Reply